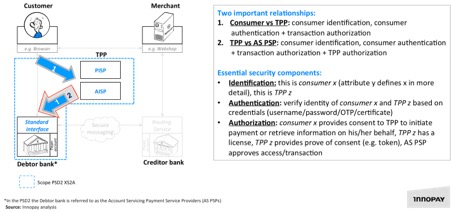
PSD2 –which is driving the change in January 2018– rules that the banks will have to open up their payment services to outside companies (Third Party Payment Service Providers – TPPs): payment initiation service providers (PISPs) on the one hand, and account information service providers (AISPs) on the other. Both services require authorization from the customers –whether private individuals or companies– and of course prior authentication.
The EU therefore seeks a payment market in Europe that is open to other actors in addition to the banks (fintech companies). In this scenario, managing users’ digital identities takes on a new dimension. This Discussion Paper from the EBA explores most of the risks and requirements of the new environment around the corner after the implementation of PSD2. It is evidently much more complex, and more sensitive. This is why APIs and the approach used to program them (open or closed application programming interfaces) is a matter for international debate.
Digital identity, a paramount asset
In the digital age, where mobile devices are now a tool for almost everything and all times, users’ data represent raw material of incalculable value. People registered with their username and password make financial transactions in real-time, associated to a first and last name, identity document, place of residence, gender, age and so on. Transactions associated to the retail sector, insurance, leisure… Not only do they provide information on expenditure, but also a record of customers’ revenues.
With the new PSD2, any company can become one of these TPPs and use the release of data to generate new income. There is no doubt that this is a race for the ownership of customers’ digital identities, and will involve hundreds of companies fighting for authorized access to this information. Europe considers it combines all the essential elements to deregulate the market and that the greatest beneficiaries will be the customers.
The components that guarantee a secure process are the following:
– Identification: definition of the attributes that confirm, beyond any shadow of a doubt, that the user is who they say they are and not someone different pretending to be them.
– Authentication: verification through credentials that the user is the customer they say they are (username and password, OTP, digital certificates and others).
– Authorization: the financial service providers (TPP) with a license to operate must be given authorization by the customers before they can access their accounts. They need to have proof of consent, which can be obtained through access tokens.
Risk-based authentication (RBA), a new ecosystem
Risk-based authentication (RBA) is the method whereby several levels of security are applied to the processes for authenticating customers or users to minimize the risk of violation. Some of the elements used in a risk-based authentication process are often the same as the ones used in some of the latest generation firewalls for classifying risk. These are:
– Role-based identification: the greater the privileges a specific user may have (for example a network administrator), the greater the risk controls they will be required to undergo. This is because they have an even greater capacity to break the protection.
– Location-based authentication: location is a key element for determining whether a transaction or bank operation entails risks or not. If the user or customer has logged on to an application or a financial service from a specific place and shortly after attempts to do the same thing from another totally different location, this may indicate an action that represents a risk to the bank and to the customers themselves.
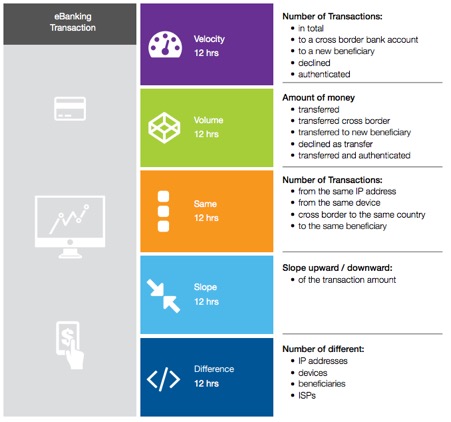
– Activity-based identification: the characteristics of some financial transactions trigger greater levels of control. Transfers involving large sums of money, transactions between accounts in banks in different companies, sending money to accounts located in tax havens…
– Habitual behavior patterns: when a user makes a transaction that is not habitual in their behavior as a customer, that action is more delicate than the ones that follow their regular behavior patterns. These tend to be detected by measuring the speed of the linked transfers, the amounts of each transaction, and so on.
– Other important elements in the systems for RBA digital identity control include type of device, IP address, status of antivirus software, and others.
Banco Bilbao Vizcaya Argentaria, S.A. owner of this portal uses cookies and/or similar technologies of its own and third parties for the purposes of personalization, analytics, behavioral advertising or advertising related to your preferences based on a profile prepared from your browsing habits (e.g. pages visited). If you wish to obtain more detailed information, consult our Cookies Policy.
Cookie settings panel
These are the advanced settings for first-party and third-party cookies. Here you can change the parameters that will affect your browsing experience on this website.
Technical Cookies (required)
These cookies are used to give you secure access to areas with personal information and to identify you when you log in.
Name
Owner
Duration
Description
gobp.lang
BBVA
1 month
Language preference
aceptarCookies
BBVA
1 year
Configuration Accepted Cookies
_abck
BBVA
1 year
Helps protect against malicious website attacks
bm_sz
BBVA
4 hours
Helps protect against malicious website attacks
ADRUM_BTs
Salesforce Marketing Cloud
Session
Required for monitoring of the service, inherent to SFMC
ADRUM_BT1
Salesforce Marketing Cloud
Session
Required for monitoring of the service, inherent to SFMC
ADRUM_BTa
Salesforce Marketing Cloud
Session
Required for monitoring of the service, inherent to SFMC
ADRUM_BT
Salesforce Marketing Cloud
Session
Required for monitoring of the service, inherent to SFMC
xt_0d95e
Salesforce Marketing Cloud
Session
Remember user preferences (if any)
__s9744cdb192d044faa1bf201d29fafd1e
Salesforce Marketing Cloud
Session
Remember user preferences (if any)
wpml_browser_redirect_test
WPML
Session
Text translation in the portal
wp-wpml_current_language
WPML
24 hours
Text translation in the portal
Analytics Cookies
They are used to track the activity or number of visits anonymously. Thanks to them we can constantly improve your browsing experience
Your browsing experience is constantly improving.
With your selection, we cannot offer you a continuously improved browsing experience.
Name
Owner
Duration
Description
AMCV_***
Adobe Analytics
Session
Unique Visitor IDs used in Cloud Marketing solutions
AMCVS_***
Adobe Analytics
2 years
Unique Visitor IDs used in Cloud Marketing solutions
demdex (safari)
Adobe Analytics
180 days
Create and store unique and persistent identifiers
sessionID
Adobe Analytics
Session
Launch's internal cookie used to identify the user
gpv_URL
Adobe Analytics
Session
Adobe Analytics plugin: getPreviousValue Capture the value of a certain variable in the following page view, in this case the prop1
gpv_level1
Adobe Analytics
Session
Cookie used to store the DataLayer levl1 of the previous page.
gpv_pageIntent
Adobe Analytics
Session
Cookie used to store the pageIntent of the previous page.
gpv_pageName
Adobe Analytics
Session
Cookie used to store the pagename of the previous page.
aocs
Adobe Analytics
Session
Cookie that stores the first values collected at the beginning of a process.
TTC
Adobe Analytics
Session
Cookie used to store the time between the App Page Visit event and the App Completed event.
TTCL
Adobe Analytics
Session
Cookie used to store the time between the LogIn event and App Completed.
s_cc
Adobe Analytics
Session
Determine if cookies are active
s_hc
Adobe Analytics
Session
Cookie used by Adobe for analytical purposes
s_ht
Adobe Analytics
Session
Cookie used by Adobe for analytical purposes
s_nr
Adobe Analytics
2 years
Determine the number of user visits
s_ppv
Adobe Analytics
Permanent
Adobe Analytics plugin: getPercentPageViewed Determine what percentage of the page a user views
s_sq
Adobe Analytics
Session
ClickMap/ActivityMap features
s_tp
Adobe Analytics
Session
Cookie used by Adobe for analytical purposes
s_visit
Adobe Analytics
2 years
Cookie used by Adobe to know when a session has been started.
Advertising Cookies
They allow the advertising shown to you to be customized and relevant to you. Thanks to these cookies, you will not see ads that you are not interested in.
The advertising is customized to you and your preferences.
Your choice means you will not see customized ads, only generic ones.
Name
Owner
Duration
Description
OT2
VersaTag
90 days
VersaTag Cookie used to store a user id and the number of user visits.
u2
VersaTag
90 days
VersaTag Cookie where the user ID is stored
TargetingInfo 2
MediaMind
1 year
Cookie that serves to assign a unique random number that generates MediaMind.
Customization Cookies
These cookies are related to general features such as the browser you use.
Your experience and content have been customized.
With your selection, we cannot offer you a continuously improved browsing experience.
Name
Owner
Duration
Description
mbox
Adobe Target
9 days
Cookie used by Adobe Target to test user experience customization.
Looks like you’re browsing from MexicoSpainArgentinaPeruColombiaBelgiumChileUSAFranceHong KongItalyPortugalUnited KingdomTurkeyUruguayVenezuelaAlemania, so let’s show you the custom content for your
location. Change
Select a country
In order to access the private area and corresponding sandbox, select the country of the APIs you want to use.